
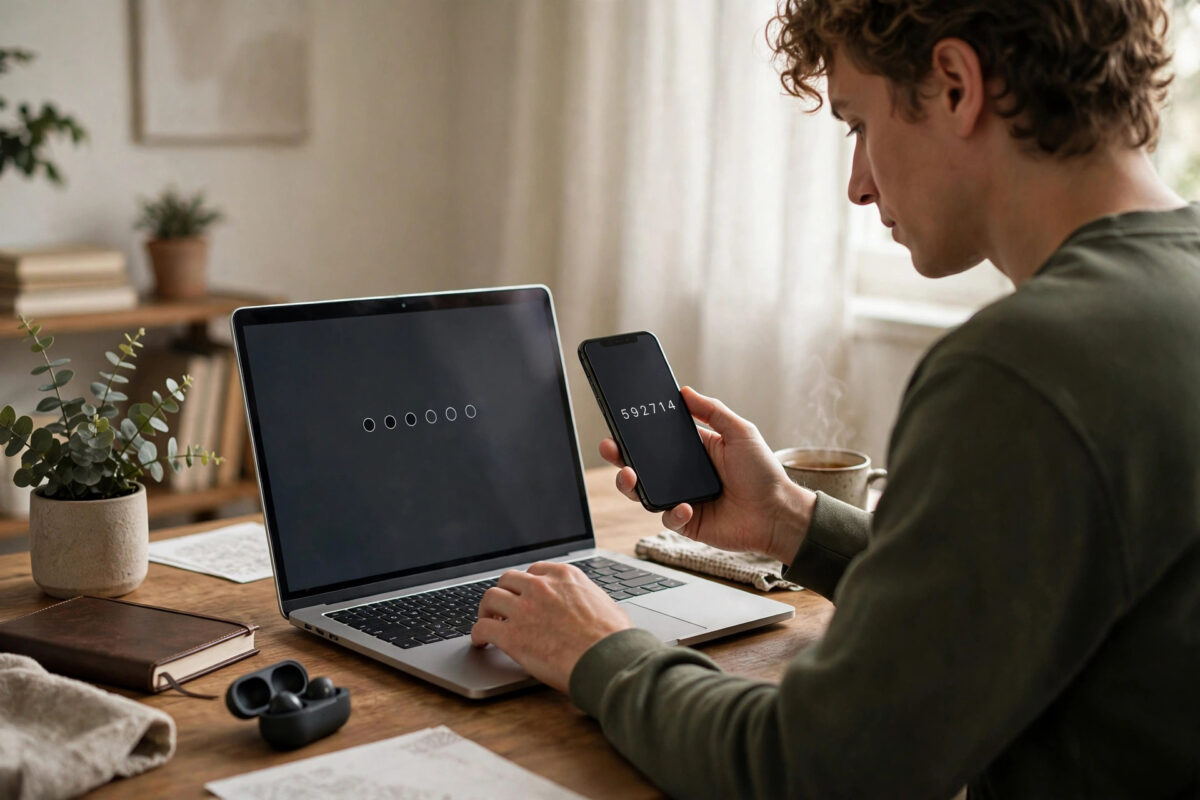
Your WordPress admin password is a single key guarding your entire website — every post, page, customer order, and setting. If that password is guessed, stolen in a data breach, or phished, whoever holds it owns your site. Two-factor authentication, usually shortened to 2FA, adds a second lock that a stolen password alone cannot open. It is one of the strongest security upgrades you can make, it is free, and it takes about ten minutes to set up. This guide explains what 2FA is, how it works in WordPress, and how to enable it safely.
Quick Answer
Two-factor authentication means logging in requires two proofs: something you know (your password) plus something you have (a six-digit code from an authenticator app on your phone, which changes every 30 seconds). In WordPress you enable it with a plugin such as Wordfence or WP 2FA: install the plugin, scan a QR code with an app like Google Authenticator, and from then on you enter a fresh code after your password at every login. Even if hackers steal your password, they cannot get in without your phone.
Why Passwords Alone Are Not Enough
Passwords fail in predictable ways. People reuse them across sites, so one breach at an unrelated service hands attackers a working password for your WordPress login — and bots test leaked password lists against wp-admin pages automatically, day and night. Weak passwords get guessed by brute-force tools that try thousands of combinations. And phishing pages trick even careful users into typing their password into a fake login screen.
2FA neutralises all three. A guessed or stolen password is useless without the second factor, and the code changes every 30 seconds, so even a code glimpsed once is worthless almost immediately. This is why security professionals treat 2FA as a baseline rather than an optional extra — it sits alongside the other login-hardening steps in our guide on how to protect your WordPress login page from attacks.
The Types of Second Factor
- Authenticator app (TOTP) — recommended. Apps such as Google Authenticator, Microsoft Authenticator, or Authy generate time-based codes on your phone. They work offline, cost nothing, and are very secure.
- Email codes. The site emails you a code at login. Better than nothing, but weaker — if your email is compromised, so is the factor — and email delivery delays can lock you out.
- SMS codes. Codes by text message are falling out of favour because phone numbers can be hijacked through SIM-swap fraud. Use an app instead where possible.
- Backup codes. A set of one-time codes you store safely (printed or in a password manager) for the day you lose your phone. Every good setup offers these — save them.
- Security keys / passkeys. Physical keys and modern passkeys are the strongest option and increasingly supported by security plugins, though authenticator apps remain the practical standard for most sites.
How to Set Up 2FA on WordPress, Step by Step
- Install your authenticator app (Google Authenticator or Authy) on your phone first.
- In WordPress, go to Plugins → Add New and install a trusted 2FA solution: WP 2FA (dedicated and beginner-friendly) or Wordfence (if you already use it for security, its 2FA is built in).
- Activate the plugin and open its setup wizard or your user profile’s 2FA section.
- Choose the authenticator-app method. A QR code appears — open your app, tap +, and scan it. The app now shows a six-digit code for your site, refreshing every 30 seconds.
- Enter the current code in WordPress to confirm the connection works.
- Save your backup codes immediately — download or print them and store them somewhere safe, outside your phone.
- Log out and log back in to experience the full flow: password first, then code. Confirm everything works before you rely on it.
- Decide your policy: at minimum, enforce 2FA for all administrator accounts. For larger teams, extend it to editors and shop managers too — anyone who can publish or change settings.
The official WordPress security guidance at WordPress.org’s hardening guide also recommends two-factor authentication as part of a sensible baseline for any site.
What Happens If You Lose Your Phone?
This is the fear that stops people enabling 2FA, and it is fully manageable:
- Use a backup code. Each code works once and gets you in to reconfigure 2FA on your new phone. This is why saving them is non-negotiable.
- Use an app with encrypted backup. Authy and most modern authenticators can restore your accounts on a new device after identity verification.
- Ask another administrator. If your site has a second admin, they can reset your 2FA from your user profile.
- Last resort — FTP. Renaming the 2FA plugin’s folder via FTP or your host’s file manager disables it so you can log in with password only, then reinstall and set it up again. Keep this knowledge private; it is an escape hatch, not a routine method.
Should Every User on Your Site Use 2FA?
Prioritise by power. Administrators absolutely — they can install plugins and change anything. Editors and authors should, because a hijacked author account can publish spam or malicious content under your brand. Shop managers handle customer data, so yes for them too. Ordinary subscribers and customers pose little risk, and forcing 2FA on them usually adds friction without meaningful benefit — though WooCommerce stores sometimes offer it as an option for customer accounts. Requiring 2FA for staff roles while keeping checkout smooth for customers is the balanced 2026 standard.
Common Mistakes to Avoid
- Not saving backup codes. The single most common 2FA disaster is self-inflicted lockout. Store codes in your password manager or a printed envelope the moment they are shown.
- Enabling 2FA but keeping a weak admin password. 2FA is a second lock, not a replacement for the first. A strong, unique password still matters — keep it strong and unique, and change it the safe way from your profile settings.
- Using SMS when an app is available. SIM-swap attacks make text codes the weakest mainstream option. Prefer the authenticator app.
- Forcing 2FA on a site with broken email and no backup plan. If your only recovery path is email codes and your site’s email lands in spam, you have built yourself a trap. Choose the app method and keep backup codes.
- Assuming 2FA makes the site invincible. It protects the login. You still need updates, backups, and sensible plugins — 2FA is one layer of several.
Conclusion
Two-factor authentication turns your WordPress login from a single point of failure into a genuinely hard target: a stolen password alone gets an attacker nothing. Setting it up with an authenticator app and a good plugin takes about ten minutes, costs nothing, and the small daily effort of typing a six-digit code is a trivial price for that protection. Enable it for every administrator today, save your backup codes properly, and one of the most common ways WordPress sites get hacked simply stops working against yours.
Frequently Asked Questions
Is two-factor authentication free for WordPress?
Yes. Authenticator apps are free, and capable 2FA plugins — WP 2FA, Wordfence’s built-in feature, and several dedicated plugins — offer their core protection in free versions. Paid tiers mainly add team policies and extra methods, which small sites rarely need.
Will 2FA slow down my login or annoy my team?
It adds about ten seconds: open the app, type six digits. Most people stop noticing within a week. For teams, the plugin settings let you add a short grace period on new devices and trusted-device options on some premium plans, balancing convenience with security.
What if I do not have a smartphone?
Desktop authenticator apps and most password managers (such as Bitwarden or 1Password) can generate the same time-based codes. Email codes are a fallback option in most plugins. A hardware security key is another route if your chosen plugin supports it.
Does 2FA protect against all hacking attempts?
No single measure does. 2FA specifically defeats password guessing, credential stuffing, and most phishing of login details. Attackers can still try exploiting outdated plugins or themes, which is why updates and backups remain essential alongside it.
Can I turn 2FA off later if I change my mind?
Yes. You can disable it for your account inside the plugin settings while logged in, or deactivate the plugin entirely. Just understand that removing it re-opens the door to every password-based attack described in this guide — most site owners keep it permanently once they are used to it.
Leave a Reply